
Premium Content
CORS and CSRF Reviewer
This prompt — CORS and CSRF Reviewer is premium. Purchase once to unlock the full prompt forever.
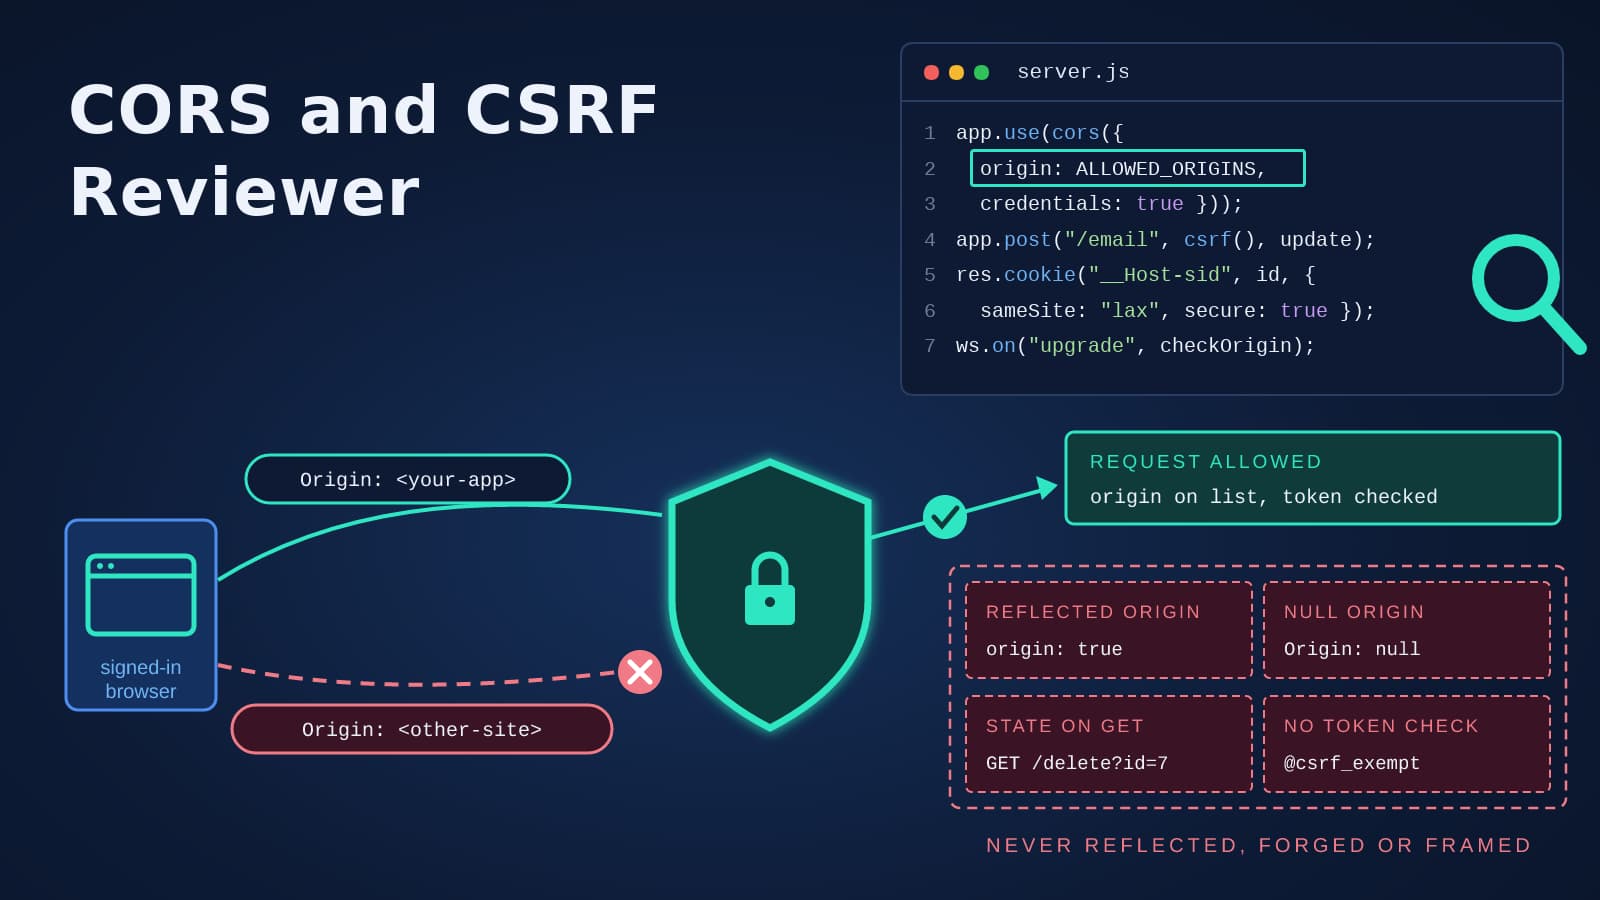
Reviews the code and settings that decide what another website can do with a signed-in user's browser before you merge - CORS middleware, CSRF protection and its exemptions, session cookie attributes, state-changing routes, method override, WebSocket upgrades and framing headers: can another site make the browser change something with the user's cookies, and can it read what comes back. Catches origins reflected or allowed as null with credentials, origin checks by prefix, suffix or loose regex, trusted subdomains, missing Vary: Origin, unprotected or exempted routes, state changes on GET, CSRF checks skipped by content type or method override, defences resting only on SameSite, cookies a subdomain can overwrite, login CSRF and WebSocket handshakes with no Origin check, then gives the smallest code that closes each path and the requests to try before merging.
What you get