
Premium Content
XSS and Content Security Policy Reviewer
This prompt — XSS and Content Security Policy Reviewer is premium. Purchase once to unlock the full prompt forever.
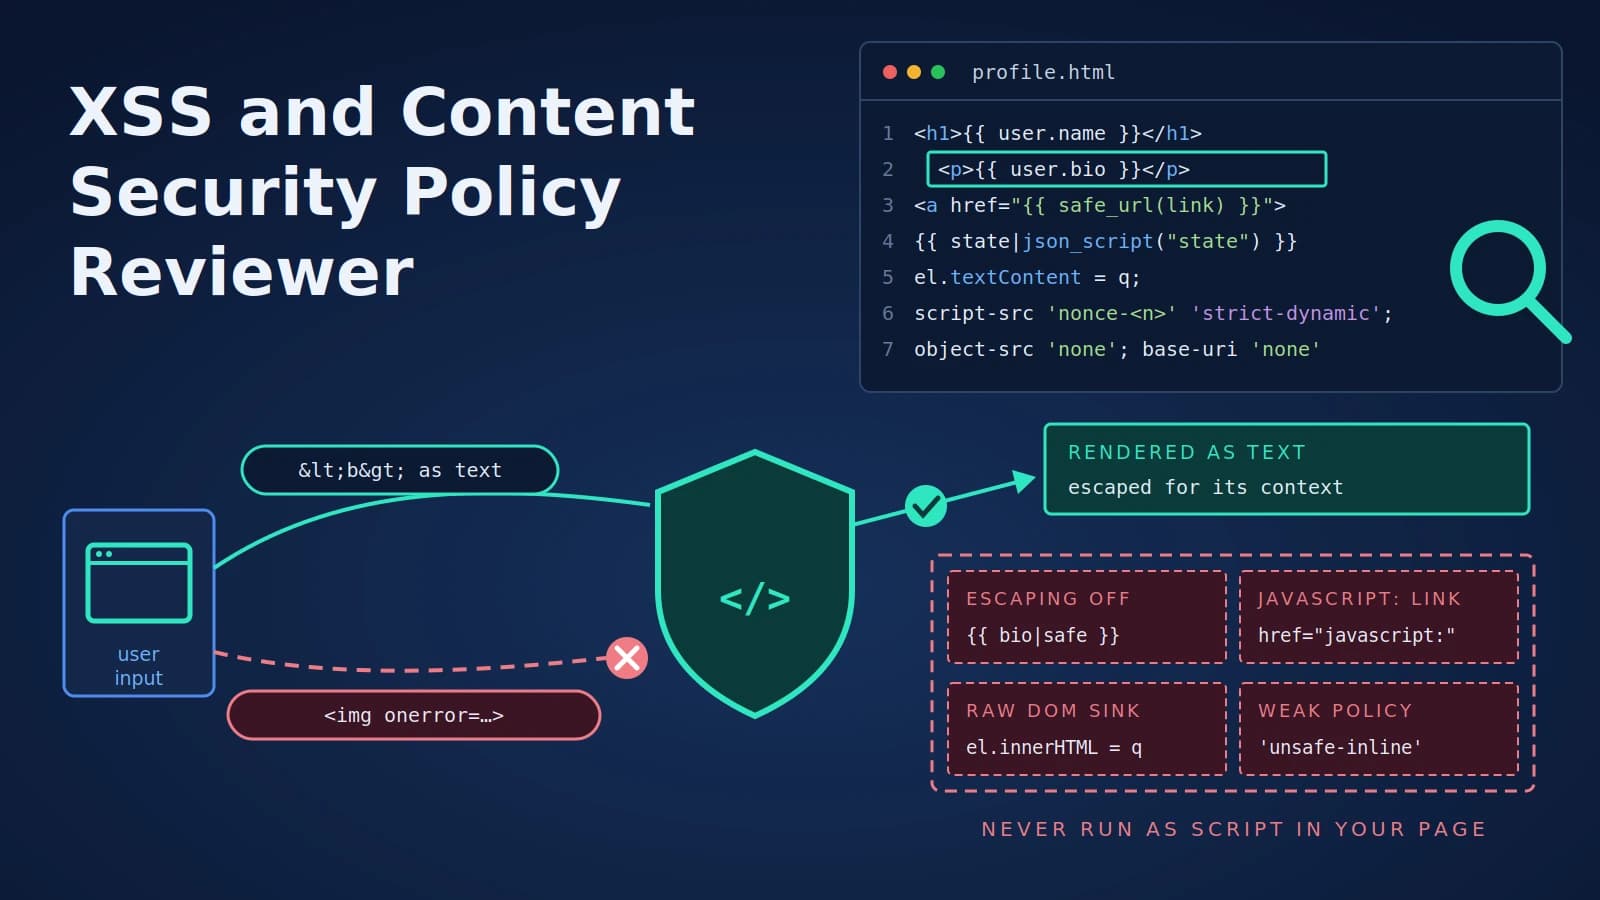
Reviews the code that puts data into web pages before you merge - server templates, React, Vue, Angular and Svelte components, DOM writes, Markdown and rich-text rendering, HTML sanitizers, JSON embedded in pages, postMessage handlers and the Content-Security-Policy header: can someone other than the user make the page run script, and what would that script get. Catches escaping turned off with |safe, html_safe, {!! !!}, dangerouslySetInnerHTML or v-html, HTML escaping used in script, URL or event handler contexts, javascript: links, innerHTML and eval sinks, JSON that breaks out of a script tag, template injection, Markdown that passes raw HTML, sanitizers misconfigured or applied too early, postMessage without an origin check, and policies weakened by unsafe-inline, allowlisted hosts, reused nonces or report-only mode. Returns a verdict, a finding table rated by who sets the value and what script gets, the attack paths, the smallest fix, checks to run before merge, and what to look for if it is already live.
What you get