
Premium Content
Cryptography Misuse Reviewer
This prompt — Cryptography Misuse Reviewer is premium. Purchase once to unlock the full prompt forever.
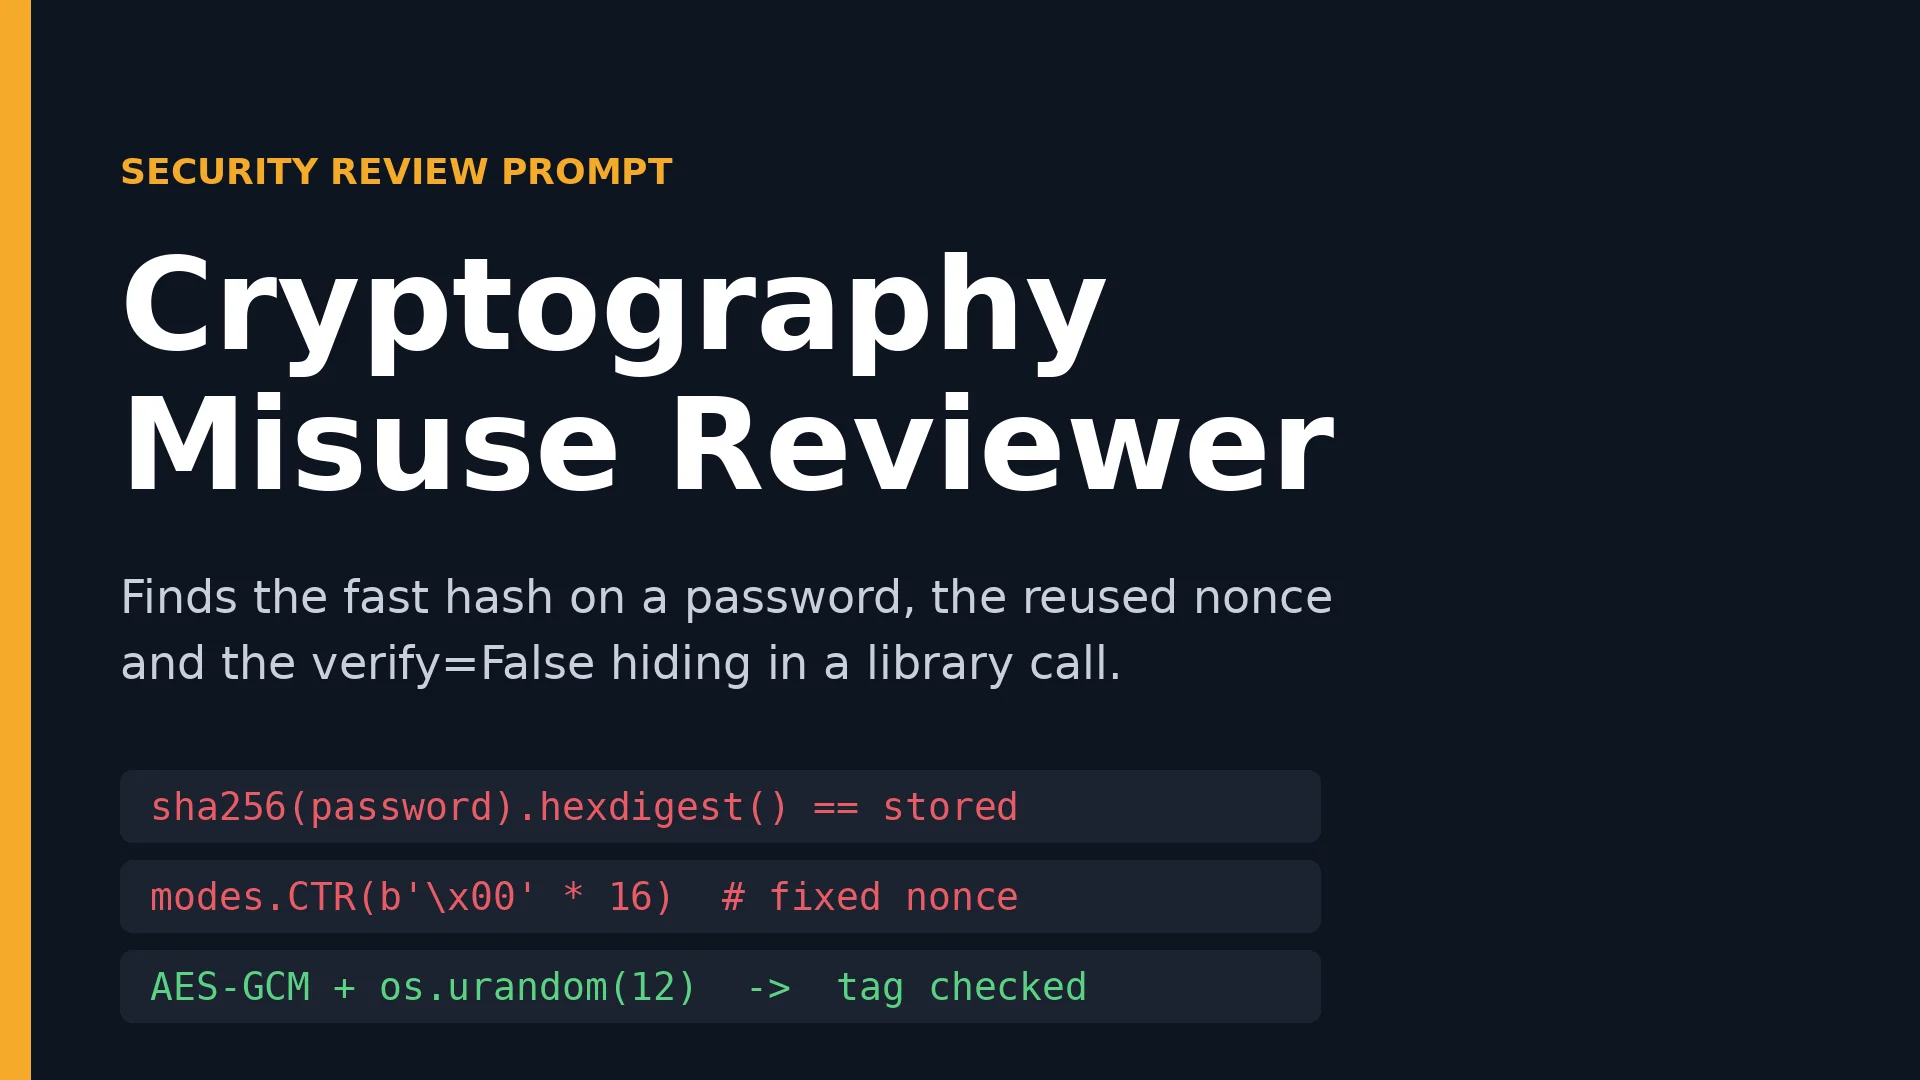
Reviews application code that hashes passwords, encrypts fields, signs or verifies tokens, generates secrets, or opens TLS connections. Paste the code, the library and its version, and where keys come from to find fast hashes on passwords, ECB or unauthenticated encryption, reused nonces, predictable random values, keys in source or logs, signature checks that compare with ==, and TLS verification turned off. Returns a verdict, a map of every cryptographic operation, evidence-linked findings, the smallest safe fix in the supplied library, and checks that prove it. Written for backend developers who ship login, payment, token, and data-at-rest code. States the library behavior, key storage, and threat model it does not see instead of inventing them. A code review prompt, not a cryptanalysis service.
What you get