
Premium Content
File Upload Security Reviewer
This prompt — File Upload Security Reviewer is premium. Purchase once to unlock the full prompt forever.
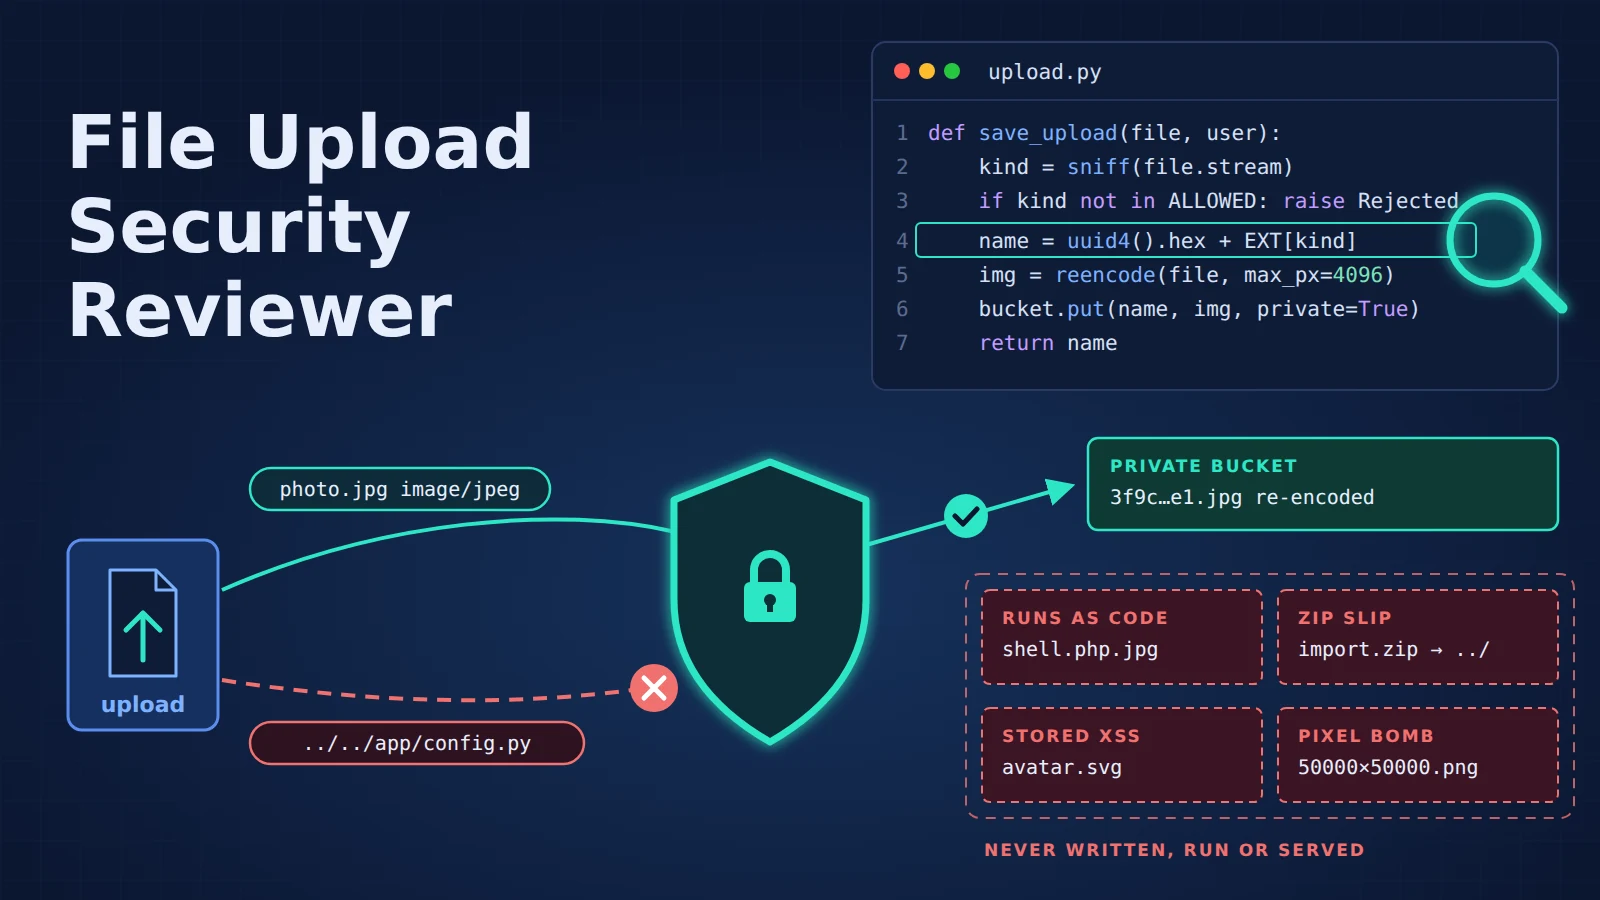
Reviews the code that takes files from users before you merge - avatar and attachment uploads, CSV and archive imports, image and media pipelines, presigned upload URLs and the routes that serve files back: can an uploaded file or its name write outside the upload folder, run as code, run a command through an image or document converter, read server files, exhaust disk or memory, or run script in your origin when someone opens it. Catches client filenames in paths, zip slip, executable folders, types trusted from Content-Type or extension, ImageMagick, ExifTool and XML entity paths, missing size and pixel limits, and files served inline from your main domain, then gives the smallest code that closes each path and the uploads to test it with.
What you get