
Premium Content
SQL and Command Injection Reviewer
This prompt — SQL and Command Injection Reviewer is premium. Purchase once to unlock the full prompt forever.
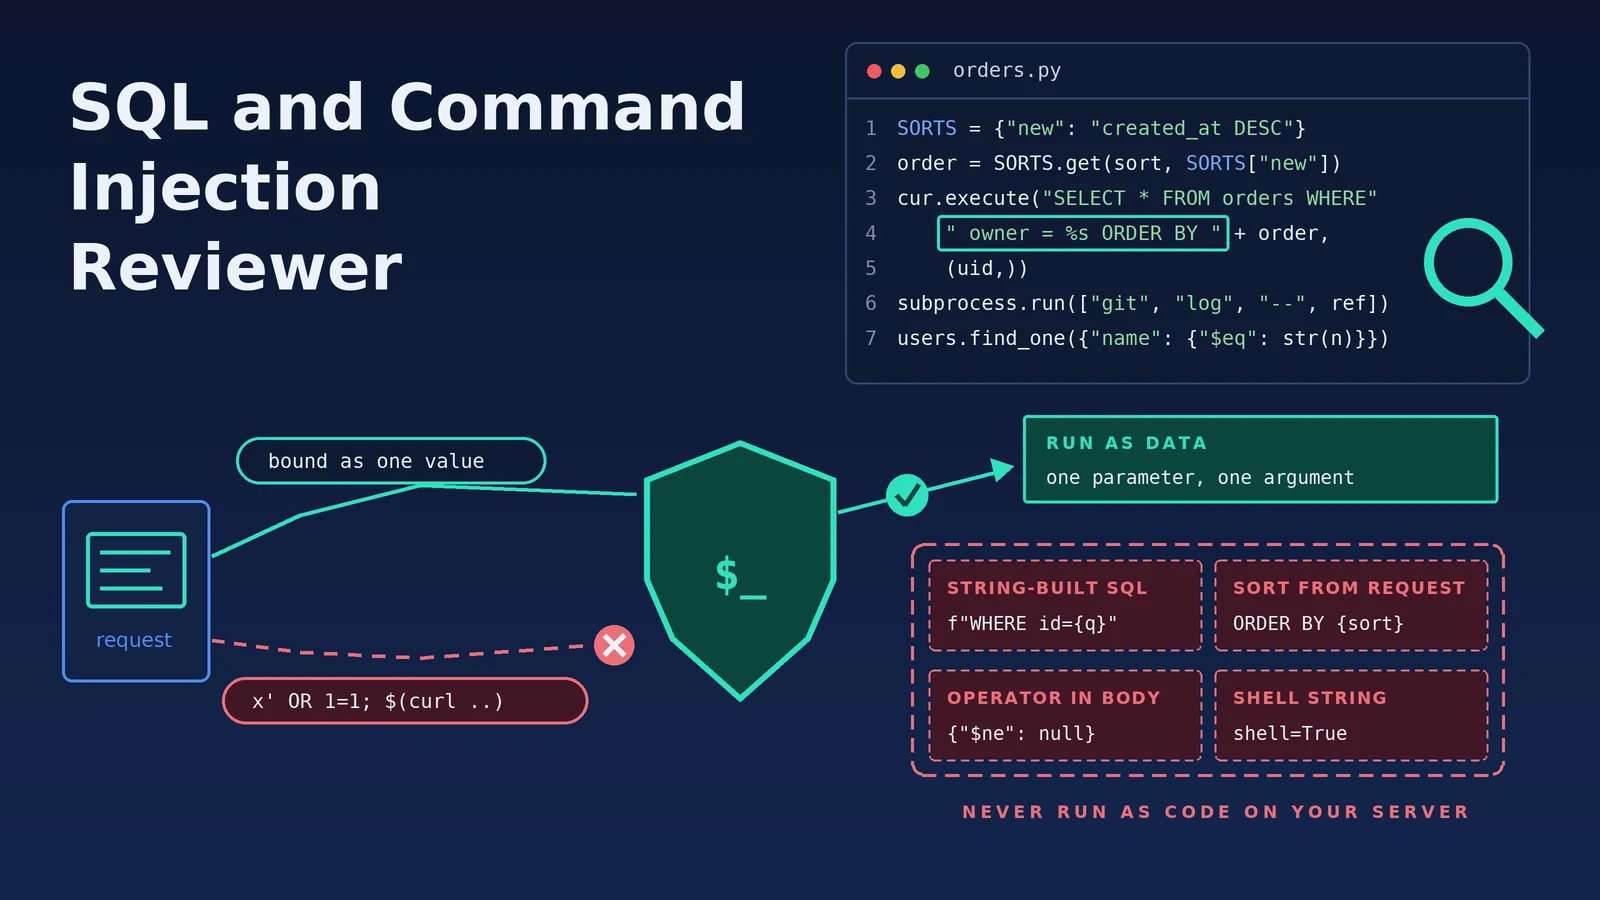
Reviews the code that builds database queries and runs other programs before you merge - raw SQL, ORM and query builder calls, stored procedures, MongoDB filters, shell and process calls, LDAP filters and eval: can a request make the server's own interpreters run something the code did not write, and what would that get. Catches values formatted or concatenated into SQL, raw ORM calls such as whereRaw, $queryRawUnsafe and FromSqlRaw with interpolation, request values used as column names or sort directions, MyBatis ${}, second-order injection, JSON bodies passed as MongoDB filters, shell=True, exec and sh -c with request values, options smuggled into git, curl or tar arguments, and eval of user input, and rates each by who can reach it and what it gets. Gives the bound, allowlisted or shell-free code that closes each path, the checks to run before merging, and what to look for if it is already live.
What you get