
Premium Content
Ship-Ready Code Audit (Any Language)
This prompt — Ship-Ready Code Audit (Any Language) is premium. Purchase once to unlock the full prompt forever.
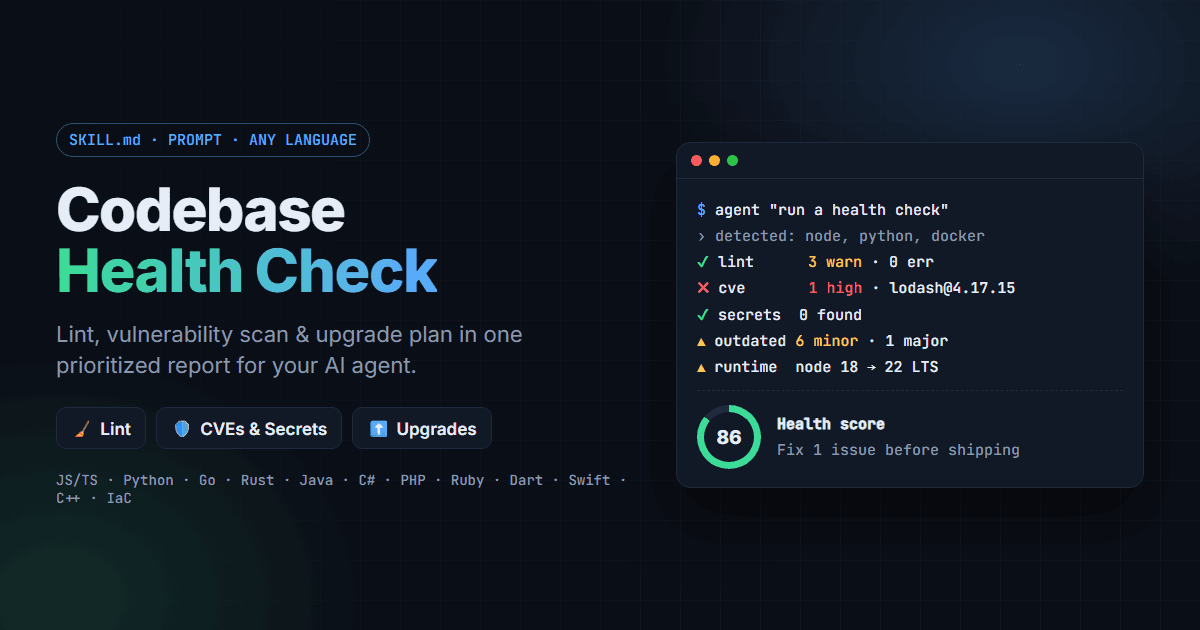
One prompt that lints, scans for vulnerabilities and plans safe dependency upgrades in any language, then delivers a prioritized report with a health score. **Stop juggling ten tools. Point your AI agent at a repo and get one ship-ready report.** Codebase Health Check is a production-grade system prompt (also shipped as an Anthropic `SKILL.md`) that turns any coding agent (Claude Code, Cursor, Codex, Swarms agents, Aider, Windsurf) into a senior engineer and AppSec reviewer. It audits the current codebase in three passes: 🧹 **Lint & Quality.** It auto-detects the stack and runs the native linter (ESLint/Biome, Ruff, golangci-lint, Clippy, dotnet analyzers, PHPStan, RuboCop, dart analyze, SwiftLint, clang-tidy, ShellCheck, hadolint, tflint…). It respects your existing configs and summarizes findings by rule. 🛡️ **Basic Vulnerability Scan.** It checks dependencies for CVEs (npm audit, pip-audit, govulncheck, cargo audit, composer audit, OSV-Scanner, Trivy), detects hardcoded secrets (and masks them in the output), and runs a lightweight SAST pass over injection, unsafe deserialization, XSS, SSRF, weak crypto, disabled TLS verification, insecure Docker/IaC/CI config. Every finding carries a severity and a confidence rating. ⬆️ **Version & Upgrade Check.** It finds outdated packages, groups them as Security / Major / Minor, flags end-of-life runtimes and frameworks (Node, Python, Java, .NET, Django, Rails, Spring…), and writes an ordered, copy-pasteable upgrade plan. 📋 **One report.** You get a summary table, a 0–100 health score, a "Fix First" top 5, detailed tables, missing-tool install hints, and a ready-to-use CI snippet so the checks run on every PR. **Built to be safe:** - Read-only by default. It never edits code or installs packages unless you ask. - It never runs your app or test suite just to audit it. - It never invents CVE IDs; unverified items are labeled. - It degrades gracefully: with no tools installed, it falls back to manual review and tells you so. - Optional **fix mode** creates a branch, applies safe auto-fixes and patch upgrades, re-runs the tests, and shows before/after scores. Major upgrades stay as a checklist. **Languages:** JavaScript, TypeScript, Python, Go, Rust, Java, Kotlin, C#/.NET, PHP, Ruby, Dart/Flutter, Swift, C/C++, Shell, Dockerfile, Terraform/Kubernetes YAML, GitHub Actions, and a manual-review fallback for anything else.
What you get